The ‘MovieReaper’ malware has infected hundreds of users, according to antivirus provider Kaspersky, which traced the attack to iTorrents.org, a site that appears to be compromised.

If you run an exe expecting it to be a movie you kind of deserve it.
I’ve gotten infections from payloads hidden in MP4 metadata before. It doesn’t have to be an exe.
payloads hidden in MP4 metadata
interesting. i wasn’t aware that was a thing.
any clue how that works? like if it targets specific video players like vlc or something?
in my head, i was just thinking that if that was the case, then on linux it might make sense for me to start using flatpak version of vlc (or use bwrap/firejail container on it).
edit: for anyone else interested in this, there are apparently a bunch of articles about it online. here’s one if you’re too lazy to look for yourself:
https://cloudmersive.com/article/How-Malicious-MP4-Files-Threaten-Security-and-Reputation
from the several articles I skimmed, it seems like it is more common to embed a batch or powershell script and target windows users, so being on Linux might help in terms of not being in the primary target demographic. But there was mention of buffer overflow techniques and such so it sounds like it really is kind of random.
And sometimes its not even technically malware but basically steganography. like the article mentioned this:
Finally, the possibility of hidden NSFW content (including CSAM and other extremely sinister illegal media) within video files can’t be ignored.
That last part would actually bother me a LOT more than some windows-specific malware on my non-windows systems. I might have to start running my pirated media thru ffmpeg / etc and having it remove any metadata I don’t specifically whitelist by field and data type… at least for the stuff that doesnt come from well known release groups on popular sites.
appreciate you calling this out, PabloSexcrowbar
windows hides file extensions by default.
even so, I would think this could be easily countered with a small bit of configuration in modern versions of qbittorrent for most users.
like this for example:
So unhide them? It will still say Application under type. I’m not going to defend Microsoft doing that but it’s not like it’s a new thing or it’s hard to fix.
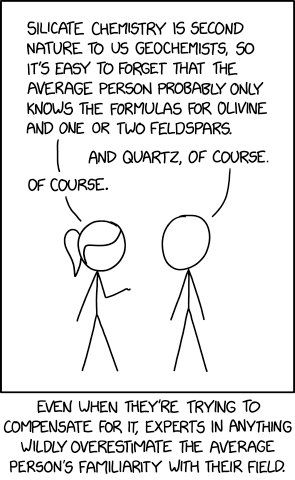
Sure, but this isn’t geochemistry it’s the most popular desktop OS in the world that the person in this scenario ostensibly owns and uses. In addition, they’re using it for the famously risky practice of piracy so you’d expect a modicum of caution.
You’ve never ever played tech support for a relative. I can tell.
I absolutely have, and if they infected themselves with The.Odyssey.2026.1080p.AMZN.WEBDL.H265.exe I would absolutely make fun of them.
Thats not very nice of you