My first thought was ripping apart something like an Apple IIe ribbon cable.
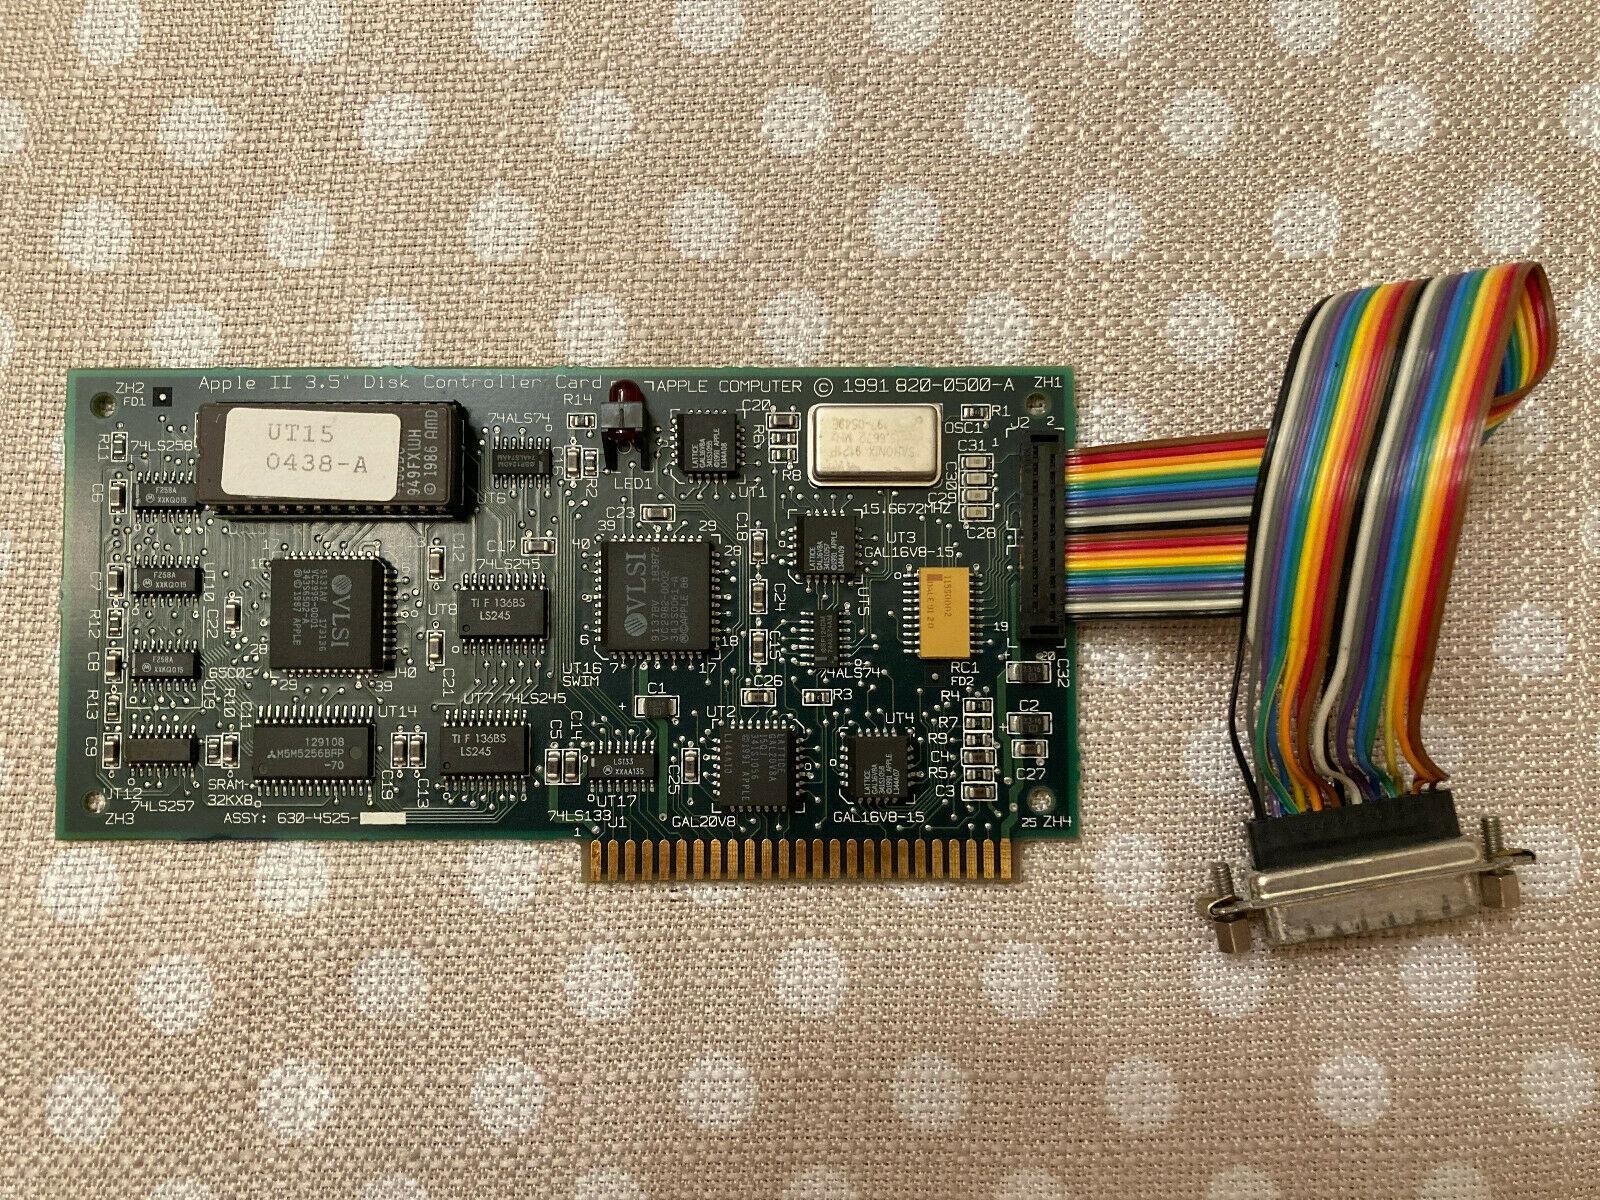
My first thought was ripping apart something like an Apple IIe ribbon cable.
At work, I used ssh-signed certificates for Linux server access - those certs are only valid for about 15 minutes.
The whole idea of shorter lifetime certificates is to address if a certificate is compromised. (Especially for client certificates which, iirc, Let’s Encrypt no longer offers).
For a home lab? With no externally accessible services? Short-lived certs aren’t really a big deal. Nobody is going to be hacking your homelab, stealing your private keys, poisoning your internal DNS, and pointing you to a different, malicious service.

It’s expensive. Sure you can start off with an old laptop, but soon you’ll want external storage to hold more images/media.
Then you’ll realize that if you just got a dedicated mini-pc you could host more containers. Oh! What if you get multiple identical PCs and then you cluster them for HA/zero downtime maintenance?!
Shit, but then you would need more than the little integrated 4 port switch on your Netgear router.
No matter! Switch to a virtualized pfsense, ditch the Netgear router and go for a 12 port switch.
Smash cut to a few years later when you’re spec’ing fiber switches/SFP+ for 10Gbps and Proxmox nodes with an extra 4GB ram so your ceph cluster doesn’t fall over randomly… Wait, why is my electric bill now $400/mo?
I’ve been seriously considering downgrading my homelab, but at this point between the *arr stack and Immich, I’m not sure if I can.