cross-posted from: https://piefed.world/c/private/p/1471349/heres-what-telegram-giving-data-to-the-u-s-government-looks-like
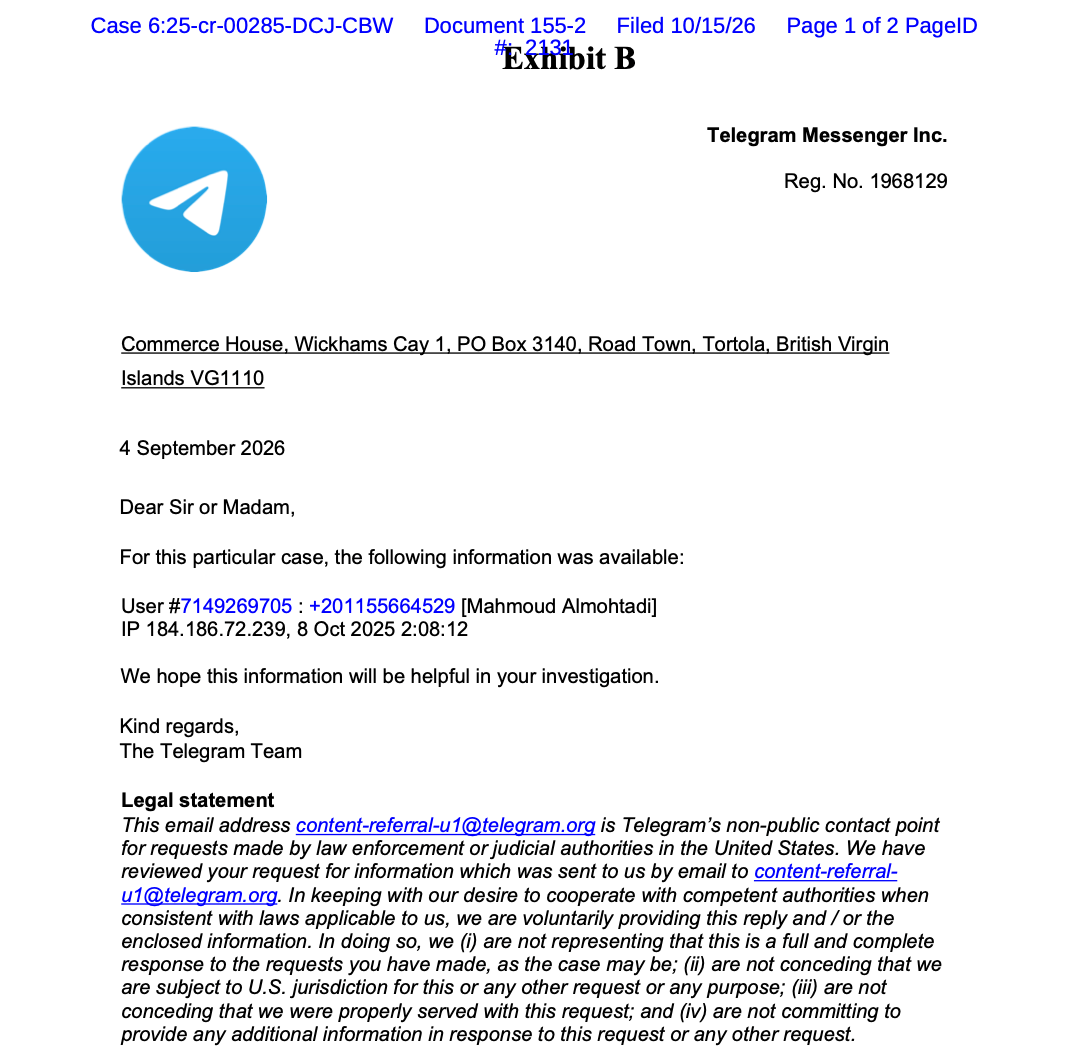
Source: Legal Document.
The case this document surfaced in centers around Mahmoud Amin Ya’qub Al-Muhtadi, who allegedly participated in the October 7 attacks against Israel.
That’s at least three points of data we know Signal can’t and won’t share.
- Phone number from ID
- Account name
- IP address
- Registration date or, worse, date this information was accurate (suggesting a ledger of changes)
lmao who told you that?
The data Telegram is sharing is right there
And we know Signal doesn’t and can’t because of its architecture and we’ve seen similar letters they had unsealed
You seem to be confused about what Signal protects against, or claims to protect against.
None of the items from your list apply. Maybe you’re confusing it with another distributed solution with peers connected through anonymous transport.
thats cool
I’m still not going to use a platform with a closed source back end.
From a purely opsec standpoint, it doesn’t really matter whether the backend is open source or not. Either way you can’t know what kind of data is being shared and whether metadata is being deleted or not. What actually matters is that the client is open source and thoroughly reviewed by independent 3rd parties. With a good messaging app, it shouldn’t matter what runs on the server. And it is known that Telegram’s client uses some weird in-house crypto and doesn’t encrypt chats by default.
This is why I’m not going to ditch Threema, even though its backend isn’t open source. I think they have a solid business model, which is why I support them. I still prefer Signal though.
Yes, but open backend means you can self host
Open source means you can audit how the application transfers data. Of course you can’t audit parts of infrastructure and data retention, but you would be able to know if they’re using an outdated dependency or if they’re not using a good encryption algorithm if they’re running an open source project.
Especially from a US company like telegram?
telegram is a russian company, though you’re from ml so you definitely knew that.
Telegram (also known as Telegram Messenger) is a Russian-Emirati … instant messaging (IM) service. https://en.wikipedia.org/wiki/Telegram_(software)
Enough said. Anyone who uses this service is a tool of the lowest level. I’ve had better screwdrivers.
That’s a hell of a combo for fucking other people’s countries up.
Eastern Europe and North Africa are in absolute tatters because of those two.
So that’s all they had on him? Or all the gov asked for?
I will have to re-visit telegrams privacy policy at some point, but aren’t they known for storing quite a lot of info (at least when compared to other private messengers like Signal?)
That’s all they are willing to share publicly. They could easily extract any normal 1:1 chat history, etc. Normal chats aren’t end-to-end encrypted.
Lol
deleted by creator